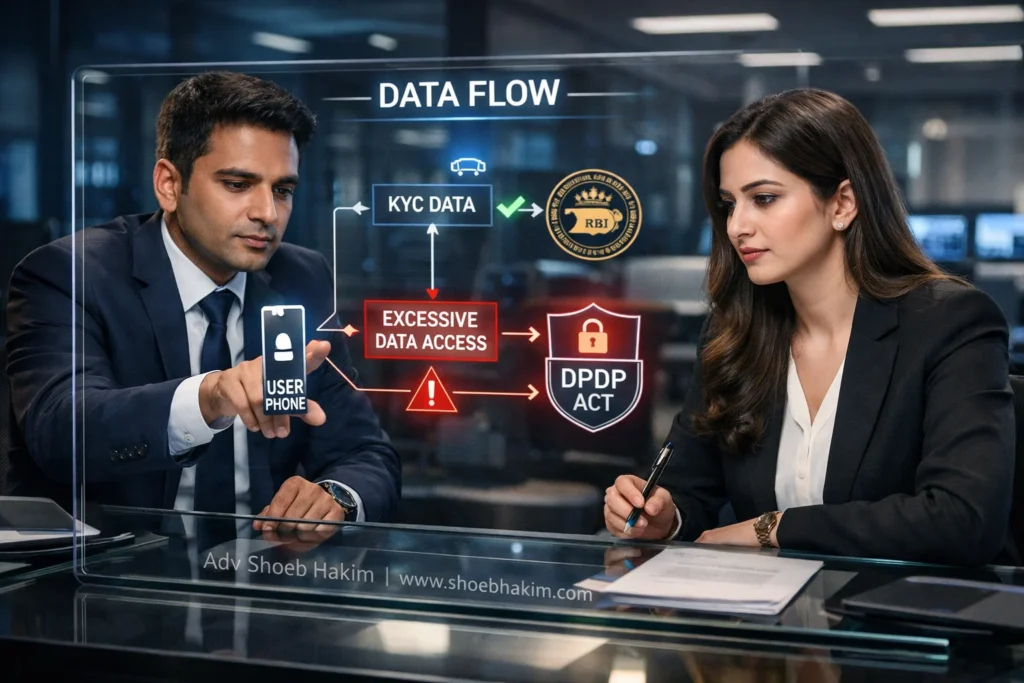
From the practitioner’s desk at Vakilverse, this PIL is a blueprint for both consumer litigation and corporate defense in digital lending disputes.
The Defense Doctrine for NBFCs/LSPs: The defense must pivot from denial to demonstrable due diligence. The primary shield will be evidence of a compliant consent architecture and proof of responsive grievance redressal. The charge of “coercive consent” is defeated by system logs showing granular, revocable permission options.

Procedural Safeguard Checklist:
- Pre-Litigation Evidence Preservation: Immediately initiate a legal hold and create forensic images of all relevant servers, consent logs, and LSP communication upon receiving any legal notice or regulatory query.
- BSA Section 63 Certification: Ensure all digital evidence (app version histories, permission logs, data access records) presented in your defense comes with a proper Section 63 BSA certificate from a certified forensic expert.
- Challenge Standing & Exhaustion: Scrutinize if the complainant exhausted the mandatory grievance redressal mechanism with the nodal officer and the RBI Sachet portal before approaching the court.
Practitioner Insight:
“In cross-examining digital lending cases, I target the gap between the app’s public privacy policy and its actual code-level permissions. The case turns on proving the architecture forced the violation. For the defense, the only counter is an automated, tamper-proof log that shows the user had a genuine, granular choice. If your system wasn’t built to create that evidence, it was built to lose this case.”